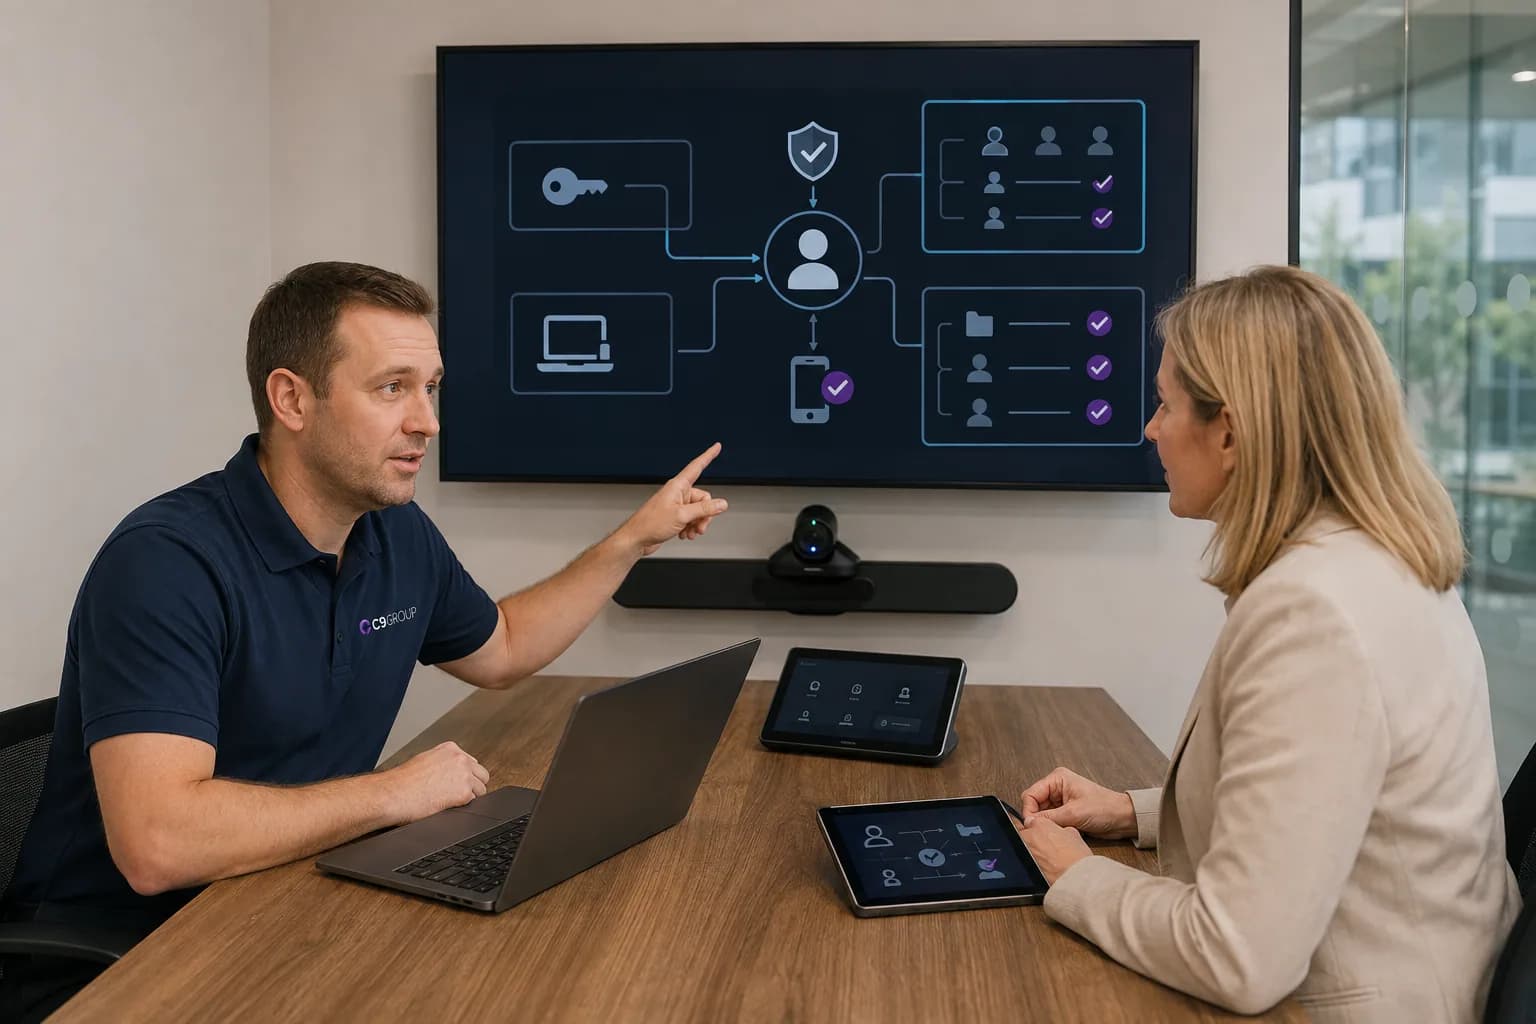
Access is added faster than it is reviewed.
People receive access when a need appears, but old permissions can remain after roles, projects and responsibilities have changed.
Identity is the control layer behind Microsoft 365, Teams, SharePoint, devices and everyday business applications.
Review accounts, MFA, conditional access, admin roles, guest users and employee lifecycle processes so access follows real business roles instead of accumulating over time.
Microsoft Entra ID · MFA · conditional access · admin roles · guest access · joiners and leavers
Identity issues are rarely created by one bad decision. They appear gradually as people join, move roles, leave, invite guests, share files and receive extra permissions to solve urgent work.
People receive access when a need appears, but old permissions can remain after roles, projects and responsibilities have changed.
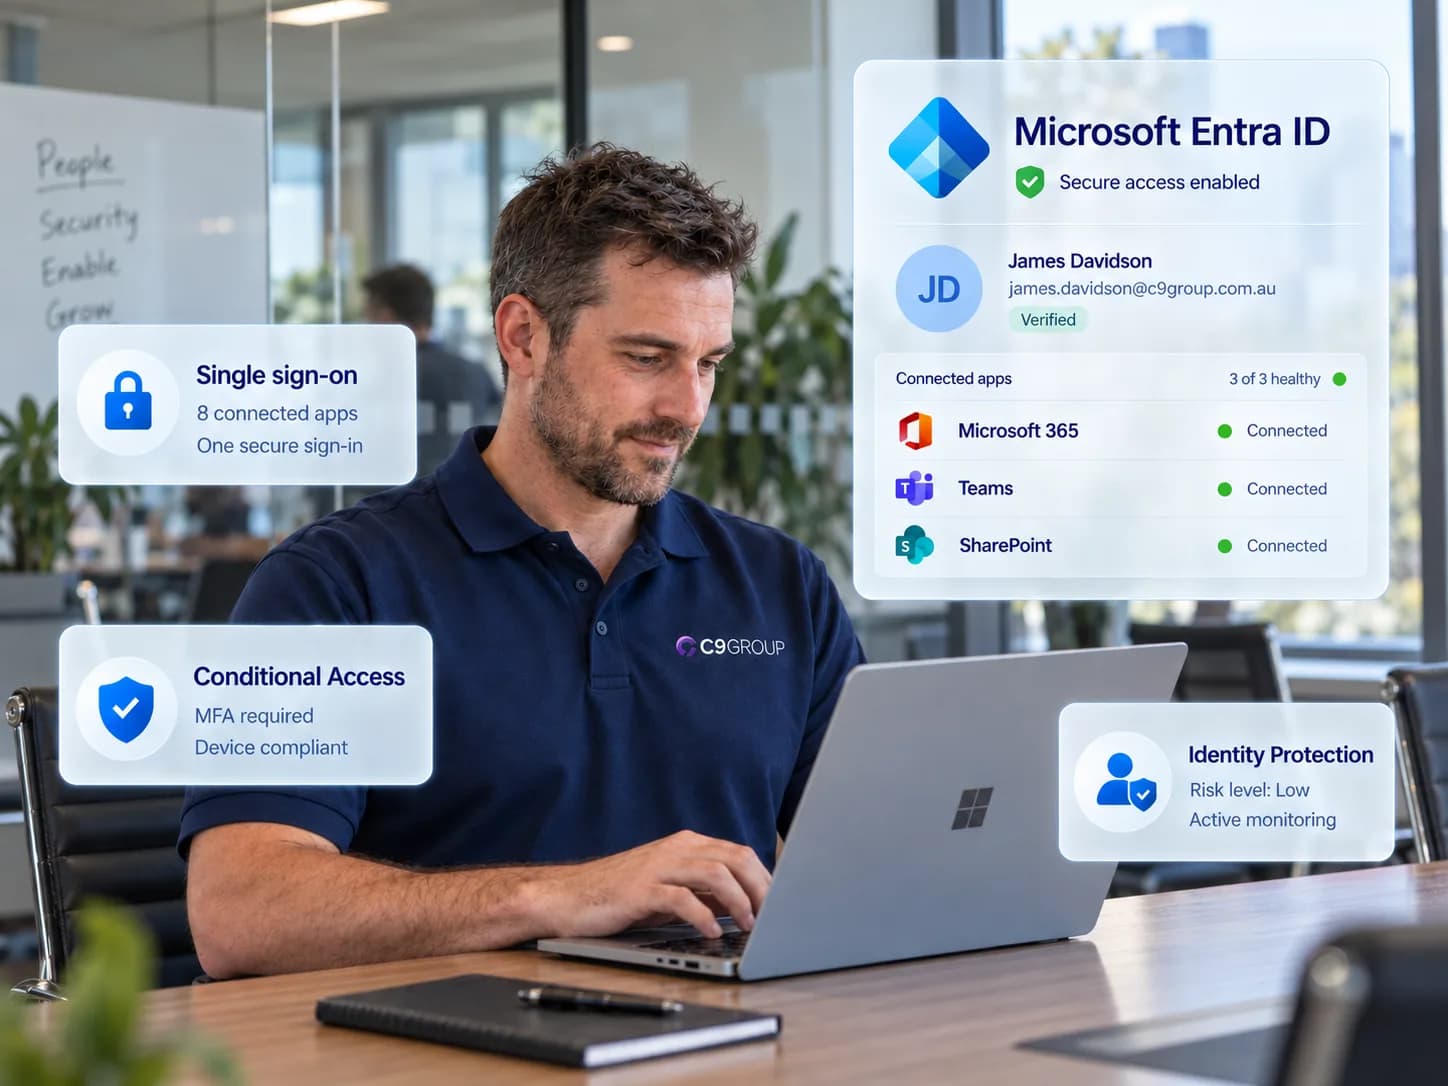
Multi-factor authentication may be switched on, yet exceptions, device trust, location rules and risky sign-in handling are not always understood.
Administrative roles are often granted to solve urgent tasks. Over time, the business may lose clarity around who can change critical Microsoft settings.
External users may be invited for valid work, then remain connected to Teams, SharePoint or Microsoft groups after the relationship has changed.
When someone leaves, access removal can rely on manual checklists rather than a repeatable process across accounts, devices, groups and shared files.
The problem is rarely that a business wants loose access.
The problem is that access keeps changing faster than anyone reviews it.
Good identity management is not about blocking work. It is about making access deliberate enough that people can trust it.
Identity and access decisions sit underneath Microsoft 365, Teams, SharePoint, devices and security. Managing them properly means reviewing the accounts, policies, groups and admin paths that decide what people can reach.
Microsoft Entra ID
Review how accounts, groups, authentication and access policies are structured across the Microsoft environment.
MFA
Review MFA coverage, exceptions and user experience so authentication helps protection without becoming a daily workaround.
Conditional access
Review policies around users, roles, locations, device state and risk signals before access is granted.
Users and groups
Review users, groups and access assignments so permissions can be explained without relying on guesswork.
Admin roles
Review privileged roles and administration paths so critical settings are not controlled by more people than required.
Joiner mover leaver
Create clearer processes for new starters, role changes and departures across accounts, groups and Microsoft services.
Guest access
Review guests, suppliers and partners across Teams, SharePoint and Microsoft groups so access remains tied to real work.
Inactive access
Identify stale accounts, unused access and old external relationships before they become harder to explain.
Ongoing change
Review access policies and identity controls as the organisation grows, restructures or introduces new Microsoft capabilities.
Security tools matter, but access control starts with the identity model underneath them.
When identity is organised, Microsoft 365 becomes easier to manage, secure and scale.
Identity work should begin with your current Microsoft environment: users, groups, MFA, conditional access, guests, admins, internal IT ownership and the access decisions people make every week.
Review current users, groups, MFA, admin roles, guest access and conditional access before adding new security tools.
A clearer joiner, mover and leaver process helps accounts, groups and permissions stay controlled as more people join.
Guest users, shared files and project access need review paths so external collaboration does not quietly remain open.
Keep your internal team close to access decisions while adding policy review, clean-up and Microsoft Entra support where needed.
Identity is not finished once MFA is enabled or the first conditional access policy is created.
People join. People leave. Roles change. New apps are added. Guests come and go. Microsoft capabilities evolve.
Ongoing management keeps access from quietly drifting away from the way the business actually works.
The aim is not to make sign-in complicated. It is to make access controlled enough that the business can explain it.
The commercial value is practical: clearer access ownership, cleaner employee lifecycle processes and a stronger Microsoft foundation for collaboration, files, devices, security and Copilot readiness.
People can explain who has access, why they have it and who should approve changes.
Access follows a repeatable process when employees join, move roles or leave the business.
Authentication settings, exceptions and user experience become easier to understand and improve.
Privileged access can be reviewed so critical Microsoft settings are limited to appropriate roles.
Guests and suppliers are easier to see, review and remove when the business relationship changes.
Teams, SharePoint, devices, security and Copilot readiness all depend on identity being organised underneath.
If users, guests, admins, MFA rules and permissions have grown with the business over time, start by understanding the identity layer before adding more tools or changing policies.
Know what should stay, what should be cleaned up and what needs attention first.
Choose which optional analytics and live chat tools C9 GROUP may use. You can change this later from the footer.